Ninety Days to Ready: Turning Regulatory Scramble into a Quarterly Operating Rhythm
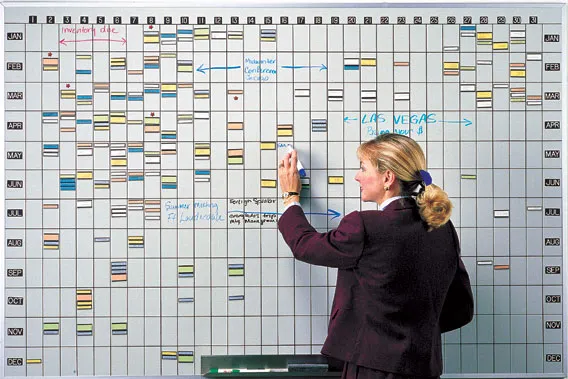
Photo: calendar planning compliance deadline office whiteboard 90 day, via www.magneticconcepts.com
The pattern repeats with each new privacy law that takes effect in an American state. In the weeks before the deadline, enterprises commission a rapid assessment. The assessment finds the same things it found last time: consent records incomplete, data flows undocumented, retention rules inconsistently applied. Remediation begins under deadline pressure, costs more than it should have, and the findings file goes into a drawer until the next law forces it out.
The alternative is not a bigger compliance team. It is a fixed, repeatable 90-day cycle that treats CRM regulatory readiness the way well-run companies treat quarter-end close: scheduled, resourced, and boring. Boring is the goal. Below is the sprint structure, broken into three phases, that makes it possible.
Days 1–30: Map Before You Fix
The most common failure in compliance readiness is starting with remediation before completing discovery. Teams fix the gaps they know about while unknown gaps compound. The first month resists that instinct.
Weeks 1–2: Inventory data flows end to end. Document every path by which personal data enters the CRM—web forms, imports, integrations, sales rep entry, AI-generated records—and every path by which it leaves: marketing platforms, analytics tools, vendor APIs, exports. Most enterprises running this exercise for the first time find integrations no one has owned in years. Each flow gets an owner, a lawful basis, and a documented purpose.
Weeks 3–4: Assess against the specific incoming rules. Map the inventory against the actual requirements landing next—not privacy law in the abstract, but the specific statutes and sector rules with imminent effective dates. A data flow that is compliant today may be noncompliant under a new state's consumer rights regime, particularly around deletion, correction, and opt-out of profiling. Produce a gap register with severity ratings and named owners. This register is the sprint's central artifact; everything after this point executes against it.
Days 31–60: Remediate with Priority Discipline
Month two is where the register converts to changes in the CRM itself. The discipline is sequencing: fix by exposure, not by ease.
Consent records first. Consent defects carry direct regulatory exposure and are the most frequently cited findings. Where consent provenance is missing, backfill what can be verified from source systems and flag the remainder for re-permissioning campaigns. Where consent exists but its scope is ambiguous, narrow it—ambiguous consent is treated as no consent in most enforcement contexts.
Retention and deletion second. Configure or verify retention rules so that data older than policy limits is flagged or purged automatically. Manual deletion projects do not scale and do not survive staff turnover. The test for this phase: can the company produce, on demand, the answer to "what personal data do we hold on this individual, and why?" If that question requires a week of cross-team emails, the remediation is not done.
Access and permissions third. Reconcile CRM role assignments against current job functions. Departed employees with active credentials and reps with unrestricted access to sensitive accounts are unglamorous findings that appear in nearly every post-incident report.
Throughout the phase, every remediation action gets documented as it happens—what changed, why, when, and on whose authority. That documentation is not overhead. It is the difference between demonstrating a functioning compliance program and merely asserting one.
Days 61–90: Stress-Test and Institutionalize
The final month proves the work under pressure, because untested controls are indistinguishable from absent ones.
Run the consumer rights drill. Simulate a data subject request end to end: locate the individual's data across all systems, verify its accuracy, execute deletion or correction, and document the response within the statutory window. Time it. Most first attempts blow past the deadline not because the work is hard but because the handoffs were never rehearsed.
Stress-test reporting. Generate the reports a regulator or auditor would request—consent coverage by source, retention compliance by record type, access logs for a sample account—and evaluate them the way an outsider would. Reports full of blanks and unexplained exceptions are findings in embryo.
Run an incident tabletop. Walk through a breach scenario touching the CRM: detection, containment, notification obligations across affected states, and CRM-specific questions like whether audit trails can establish what data was accessed. Sixty minutes of tabletop surfaces gaps that ninety pages of policy conceal.
Close with the rhythm. The sprint ends with a short retrospective and a calendar entry: the cycle begins again next quarter, with the updated gap register as its starting point. Regulatory change monitoring feeds the register continuously, so each sprint begins with current requirements rather than stale assumptions.
From Sprint to Standing Capability
The first 90-day cycle is genuinely difficult, and organizations should expect it to be. The second is materially easier because the inventory exists. By the third, the question shifts from "are we ready for the next law?" to "which parts of our readiness can we productize?"—because companies with demonstrable, repeatable compliance discipline increasingly find that it functions in the market as well as in the audit file. Readiness, practiced quarterly, stops being a cost center and starts being a posture. That posture is the point.